BigCommerce Store and App Security Best Practices
Secure BigCommerce storefronts and integrations by controlling users, API credentials, app callbacks, theme code, and customer-data flows.
Guide10 min
Resource centre
Explore practical articles, in-depth guides, company updates, decision-making frameworks, and tools from the WEBSITETOON team.
Browse resources
Guides
In-depth guidance for organizations planning web and application projects, measurable marketing programs, and practical security improvements.
Secure BigCommerce storefronts and integrations by controlling users, API credentials, app callbacks, theme code, and customer-data flows.
Build a marketing program that connects customer needs, channels, content, measurement, and responsible automation.
Protect browser-facing websites by treating content, forms, scripts, embeds, and response headers as parts of one security boundary.
Reduce client- and server-side JavaScript risk through safe data handling, controlled dependencies, clear trust boundaries, and secure deployment.
Reduce web-server risk by minimizing services, restricting administration, hardening Nginx and TLS, and monitoring the deployed system over time.
Protect application data by combining database hardening with safe queries, narrow service identities, controlled networks, encryption, and tested recovery.
Protect Node.js services by controlling inputs, packages, process permissions, network behaviour, and the production environment around Express.
Secure PHP and Laravel applications by preserving framework protections, limiting runtime privileges, and maintaining the full hosting stack.
Plan a website or application around users, workflows, integrations, AI opportunities, and a successful launch and handover.
Use Django’s built-in safeguards deliberately while hardening Python dependencies, settings, data access, and the production deployment path.
Preserve React’s safe defaults while securing HTML rendering, authorization, data flows, dependencies, and the server-side code around the interface.
Design API security around identities, objects, actions, data exposure, resource consumption, and the clients and integrations that depend on them.
Protect a Shopify operation by governing staff access, apps, theme code, customer data, webhooks, and the systems connected to the store.
Strengthen application security with a practical combination of assessment, testing, hardening, protection, and continuous review.
Reduce WordPress risk by maintaining a small trusted software inventory, hardening administration and hosting, and preparing to detect and recover from incidents.
Blogs
Plain-language perspectives on building, growing, and protecting your digital operations.
Keeping WordPress, plugins and application dependencies current is only part of maintaining a secure website. The software underneath your applications needs attention too. October
Justin Merced · 2026-10-22
Multiple critical vulnerabilities have been disclosed across widely used platforms, including Check Point SmartConsole, NGINX, Firefox, OpenWrt, and VMware products. These vulnerab
Justin Merced · 2026-07-29
Several newly disclosed vulnerabilities affecting WordPress and nginx are drawing significant attention from the cybersecurity community due to their potential impact and reports o
WEBSITETOON · 2026-07-23
When business owners think of a cyberattack, they often picture something dramatic: a defaced website homepage, a lock screen demanding bitcoin, or a complete server shutdown.
Justin Merced · 2026-07-13
Every time you create a new online account, you are told to make your password "strong." But what does strength actually mean to a computer? Hackers don't guess passwords the way h
Justin Merced · 2026-07-13
Imagine building a high-tech fortress to protect your business. You install heavy iron gates, security cameras, and a state-of-the-art check-in desk at the entrance. But when guest
Justin Merced · 2026-07-13
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has expanded its Known Exploited Vulnerabilities (KEV) Catalog by adding two actively exploited security issues tha
WEBSITETOON · 2026-07-10
Security researchers have disclosed three high-severity vulnerabilities affecting the OpenClaw AI assistant that could allow attackers to steal sensitive credentials, escalate priv
WEBSITETOON · 2026-07-10
A recently disclosed software supply chain attack, dubbed "Mini Shai-Hulud," demonstrates how attackers can exploit insecure GitHub Actions workflows to compromise software package
WEBSITETOON · 2026-07-10
Company news
Updates about our memberships, community commitments, and work beyond client projects.
WEBSITETOON is a member of the Canadian Cyber Threat Exchange.
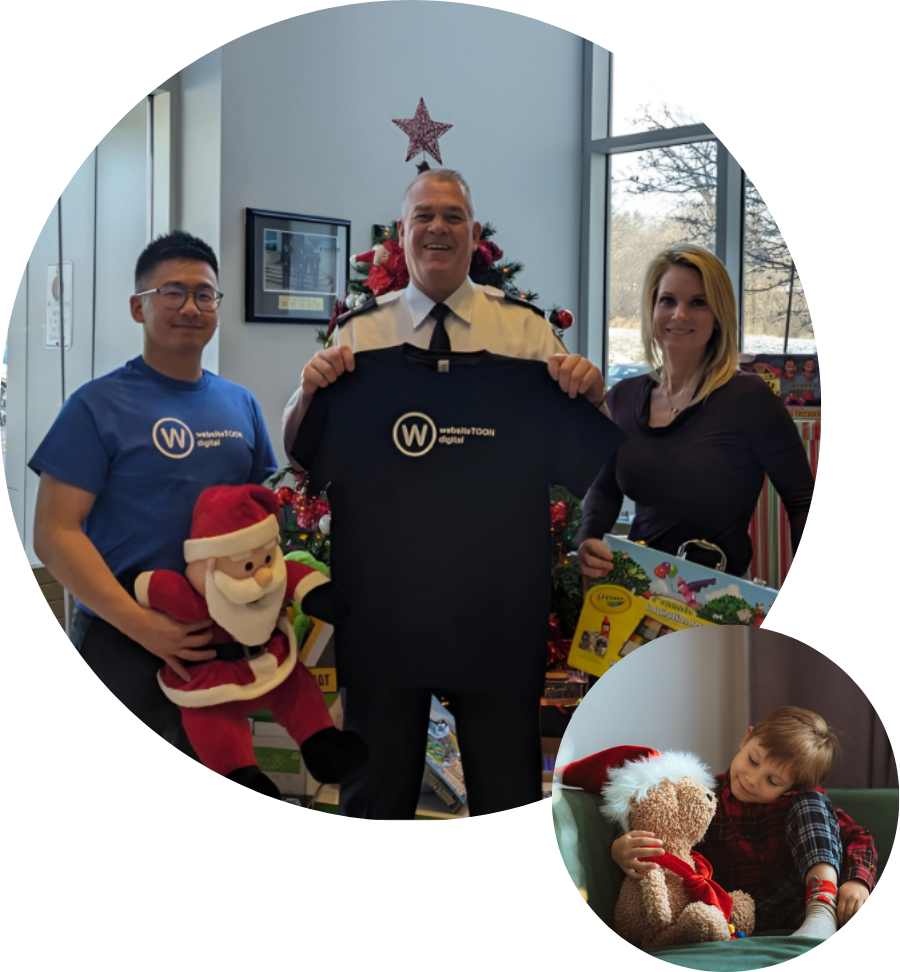
Our support for the York Regional Police Holiday Heroes program and the families, children, seniors, and vulnerable community members it serves.
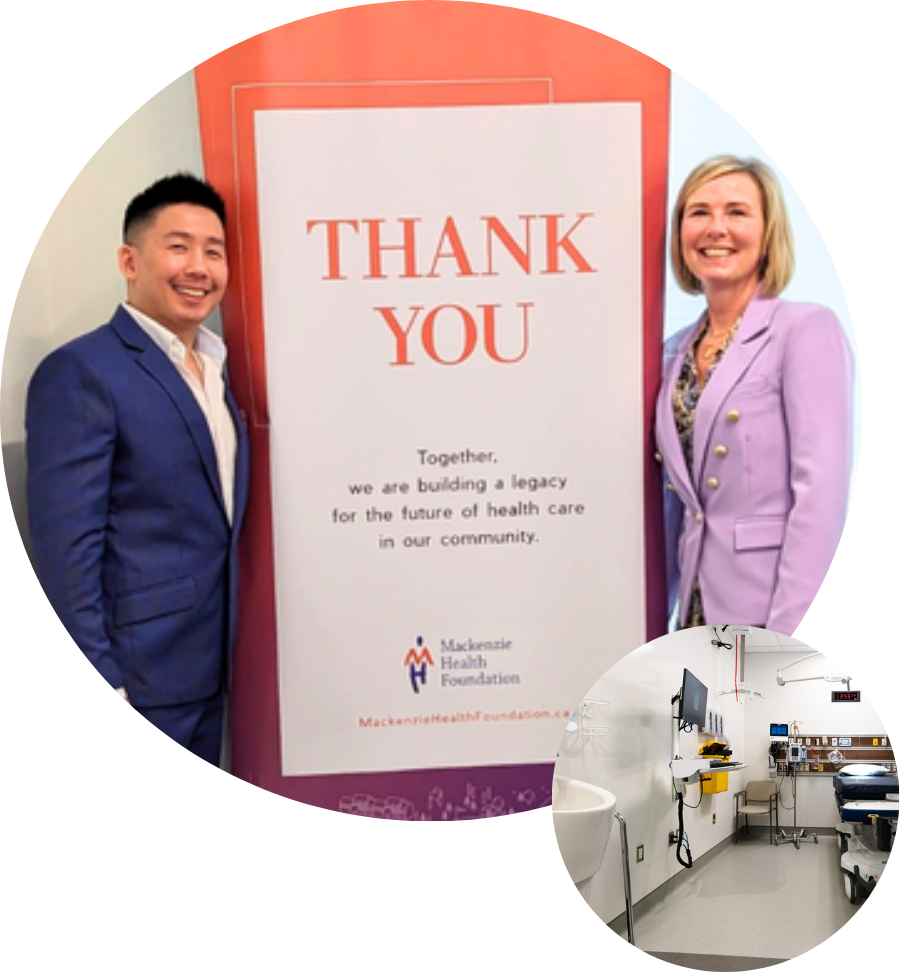
Our contribution to emergency care at Mackenzie Health, including Mackenzie Richmond Hill Hospital and Cortellucci Vaughan Hospital.
Frameworks
Use our frameworks to organize priorities, compare options, and make the next step clearer.
Profile your leads and customers by budget and urgency — and decide where to invest your marketing and R&D dollars.
Tools
Worksheets, checklists, and assessment tools will be published here as they are prepared and reviewed.
We are developing useful resources for planning web projects, evaluating marketing priorities, reviewing security readiness, and supporting employee training.